ComplyChat Start free

This page describes the organisational service. For personal messaging, see ComplyChat Free, with its consumer terms and privacy notice.

Us & the category

It comes down to shape.

Almost every product like this does the same thing with your messages: it pools every client's permanent records into the supplier's own cloud. We do the opposite. The permanent record of truth rests in your own Microsoft 365, per organisation, never in one shared vendor vault. We run the channel and hold a working copy to operate it, which you can purge after a retention window of your own choosing or, on Enterprise, hold in a dedicated database rather than the shared one. Two shapes. One of them pools everyone's record of truth. One of them doesn't.

Care colleagues exchanging an update outside a home
Everyone's record of truth in one store
The usual shape: five organisations, one shared supplier store. Five organisations stand in a row and every one of them is empty. A line drops from each, all five join a single track, and that track passes through one padlock into a single wide store below. Inside the store the five records of truth sit bunched together in a pile, the middle one, yours, among them. One store, one lock, everyone's record of truth behind it.

Every client's record of truth is copied off and pooled in the supplier's own cloud. One store, one lock: whoever gets through it has all of them.

Each record of truth in its own Microsoft 365
Our shape: five organisations, each holding its own record of truth. The same five organisations stand in the same row, and this time each one holds its own record of truth, behind its own padlock. Five dashed lines run upward, one into each organisation, from a dashed band along the bottom: that band is the channel we run and the working copy we hold to operate it, and the marks in it are outlines, not records of truth. There is no shared store. Reaching five records of truth means five separate break-ins, one at a time.

Each record of truth is handed up into that organisation's own Microsoft 365, behind its own lock. The dashed band is the channel we run and the working copy we hold to operate it – yours to purge after a retention window of your choosing, or, on Enterprise, held in a dedicated database of your own.

  • A record of truth
  • A working copy
  • One way in

The same five records of truth, drawn twice. On the left, one lock stands between an attacker and all five. On the right, reaching five means five break-ins, one at a time – and the band along the bottom holds working copies, not the record anyone answers from. The organisation marked in the middle is yours.

The usual shape

The supplier's own store

Your conversations are copied off to the supplier's servers and pooled with everyone else's. One system, one login, one place where every customer's messages sit together. It is easy to build, and easy to attack: one store, holding the lot, with a single door. The whole field was shaped this way because it was built for the largest, most heavily regulated buyers.

One vault · everyone's messages in it
Our shape

Your own Microsoft 365

Your permanent records live in your own Microsoft 365, under your own rules for keeping them, holding them and searching them. The system of record you answer from rests there, per organisation, never pooled with anyone else's – we never become your system of record. We run the channel and hold a working copy to operate it, kept for the life of your subscription unless you set a retention window of your own choosing, or, on Enterprise, held in a dedicated database rather than the shared one. There is no single shared vendor vault holding everyone's record of truth, so there is no pooled archive to lose. The working copy remains sensitive: separating customer archives does not guarantee that a compromise of our service affects only one organisation. Of the thirty-four vendors we surveyed in June 2026, twenty-five keep every client's permanent records in their own cloud. The only other architecture that leaves the record in the customer's own Microsoft 365 is Microsoft's own governance tooling – and that is not somewhere a parent can message you.

Your archive in your tenant · a separate operational working copy
26/ 34
vendors we surveyed won't publish a price. We publish ours in full, on this page.
25/ 34
pool every client's permanent records in their own cloud. Ours rests in your own Microsoft 365, per organisation, never ours – we run the channel on a working copy you control.
1at a time
is how many organisations an attacker can reach when there is no shared store to empty.
The honest trade

Here is what we are not. The big suites capture fifty, a hundred, more channels – email, voice, social, the lot – and if you must keep all of that in one place, that is what they are for. We are deliberately narrower: a few places done properly – your own channels, which people can open in a browser or reach by text, and Microsoft Teams – with the record kept in the Microsoft 365 you already have. That is the right size for a UK trustee or council board – a charity or care provider, a school or college, a chartered body or regulator – and the wrong size for a bank. We would rather do a few things well, in a shape we can stand behind, than fifty in a shape that has already been broken into once. The full story of why – the break-in that taught this whole field its lesson – is in Security, further down. Here, the point is only the shape.

Security & data protection

The safest record of truth is the one your tenant owns, not ours.

Start with the part no certificate can grant: your permanent record of truth – the SAR-answerable, eDiscovery archive – rests in your own Microsoft 365, per organisation and never pooled. We never become your system of record. The permanent record lands in your own Microsoft 365 whichever way the conversation comes in – made in our system and handed straight to your Microsoft 365 from your own channel, or captured and passed in from Microsoft Teams. To run the channel we hold a working copy of message content, which you control: set a retention window in your client portal, from 30 days to three years, after which each message's content is purged once it has been filed into your own Microsoft 365; on Enterprise the working copy is held in a dedicated database of your own rather than the shared one. A break-in at our hosted service could expose operational conversation data, including subscription history where no shorter working-copy window is set, never a permanent, pooled archive of every client – your authoritative record is in your own tenant, not on our servers. The rest is below, and where we're still earning a certificate, we say so.

01 · Custody

Your tenant owns the record of truth

Your permanent record lives in your own Microsoft 365, never pooled with anyone else's. We hold a working copy in our own systems to run the channel, and you decide how long it lasts – for the life of your subscription, or a retention window of your choosing; on Enterprise it sits in a dedicated database of your own. If you let our support team in, it is only for the moment they need, and they take no copies out of your Microsoft 365. Ask any supplier what a break-in at their end would spill. Our honest answer: your account and billing details, and at most recent operational conversation data – never a permanent, pooled archive of every client.

02 · Standards

Designed to ISO 27001

Our security is built to the ISO 27001:2022 standard from day one, across the whole of CIaaS Limited's Microsoft 365 and Azure systems – not just one corner of the product. The independent certificate is on its way, and until we've earned it we'll keep saying so plainly. A certificate shows how carefully a supplier guards what it holds – our first safeguard was to keep your permanent record of truth in your own tenant, never pooled in ours.

03 · Government

Cyber Essentials & Cyber Assurance

Targeting Cyber Essentials and IASME Cyber Assurance at whole-organisation scope (CIaaS Limited), under the UK NCSC-backed schemes. Increasingly expected by funders and public-sector partners; until certified, we say "targeting", not "certified".

04 · Residency

Your data stays in the UK

Your record lives in your own UK-based Microsoft 365. It reaches you whichever way the conversation comes in – made in your own channel and handed straight to your Microsoft 365, or passed in from Microsoft Teams – and lands in Microsoft's UK data centres. Every other company we rely on – Microsoft for hosting, calls, real-time message delivery and our own mailboxes, Twilio for the SMS verification text, Andrews & Arnold for the SMS doorbell number, and the browser push services that carry a content-free "new message" nudge – is named, with what it does and where it processes, in our published list of sub-processors. One piece is drawn outside the UK and we say so there rather than round it up: the map picture on a shared location card comes from Microsoft Azure Maps, from the coordinates alone – no identity and no IP address travels with them, and we write neither the picture nor the coordinate to any database of ours.

05 · Privacy

GDPR by design

The data protection paperwork – impact assessment, records of processing, lawful-basis analysis – arrives drafted for your circumstances, ready for your data protection lead to adapt and sign. We do the writing; you do the owning, because only you can.

06 · Transparency

We only keep what people are told about

No secret monitoring. People are on a channel the organisation owns, and they are told it is on the record. Everyone added to a channel gets a notice telling them so, and can object or leave at any time. Lawful and fair by default.

07 · Proof

If we ever touched your data, you'd know

Every organisation gets its own access feed: a content-free, hash-chained log of each time our service touches your data, plus a monthly heartbeat filed into the same folder in your own Microsoft 365 and posted to your compliance channel, confirming the chain is unbroken. It records that something happened, never what was said. The events that matter most – an access by us, a break-glass entry, an export, a change to what you keep – do not wait to be noticed: they go to the addresses you nominate, as they happen. And each night the feed's new events are mirrored to a second, append-only copy of it, held under a locked immutability policy for 395 days, so a copy of that record exists which we cannot edit or delete. The access paths and logging limitations are set out in DPA Annex D.

08 · Governance

The same rules across everything we run

ComplyChat runs inside CIaaS Limited's own Microsoft 365 and Azure systems. We set our security rules once and apply them across the Cyber Essentials, IASME Cyber Assurance and ISO 27001:2022 standards, using our own tool, Secure Compliance. We are working towards each certificate across the whole organisation – everything we run, ComplyChat included – and CIaaS Limited is registered with the ICO (ZC181640).

Why we built it this way · May 2025

In May 2025, one of the best-known names in message archiving was breached. The service ran modified versions of WhatsApp and Signal, and kept a readable copy of every client's messages on its own servers – senior US government officials' and major financial firms' alike, all in one place. The intruder reportedly needed less than half an hour. Message content was stolen, the flaw entered the US government's catalogue of actively exploited vulnerabilities, and the service was suspended.

We take no pleasure in the story – the people involved were working on the same problem we are. We retell it because the lesson is not about one company's carelessness; it is about shape. A supplier that holds everyone's records has built a single, well-signposted prize. That break-in wasn't bad luck. It was the shape.

So we built the opposite shape. The record is made in our system and handed straight into your own Microsoft 365 from your own channel, or – where the conversation runs on Microsoft Teams, no changed apps, nothing bolted on – captured and passed into the same Microsoft 365. The permanent record of truth rests in your own Microsoft 365 – with you, not us, per organisation and never pooled. We never become your system of record. To run the channel we hold a working copy of message content, which you control – kept for the life of your subscription or purged after a retention window you set, and on Enterprise held in a dedicated database of your own – and our billing systems only ever see the plan, the number of lines and whether the service is running. Our shared operational store can contain extensive conversation history, so archive separation does not remove the need to protect it. There is no single shared vendor vault pooling everyone's record of truth, so there is no pooled archive to steal.
Names, dates and sources available on the call – we'd rather argue architecture than point fingers.
Read this before buying anything in this category

What we won't promise. And nobody honest can.

We won't · 01

Read personal phones.

Nobody can, within the law. A supplier who says otherwise is selling you a data breach with a dashboard. A record can only start where ownership starts: on a channel the organisation controls.

We won't · 02

Pull in your old conversations.

A record can only cover what was on the record from the start. A channel you own has no old group to pull in – each one opens clean, on the record, and nobody – including us – can join a conversation that already exists elsewhere. So we move you forward instead, with the plan, the invites and the ready-made policies to make the switch stick.

We won't · 03

Watch anyone in secret.

Every channel is on the record and everyone on it is told so, in wording we supply; everyone added gets a notice and can object or leave at any time. Telling people is what makes the record usable as evidence and your position easy to defend.

We won't · 04

Claim nobody can read it.

Some suppliers promise that nobody – not even you – could ever read the record. A record nobody can read cannot answer a Subject Access Request: you can't have both a usable record and one nobody can read. Yours lives in your own Microsoft 365, readable by the people you choose – and we say out loud what that does and doesn't mean.

We won't · 05

Become your permanent system of record.

Your permanent record of truth lives in your own Microsoft 365, per organisation and never pooled – we never become your system of record. We run the channel and hold a working copy to operate it, which you can purge after a retention window of your own choosing or, on Enterprise, hold in a dedicated database rather than the shared one. A supplier that pools every client's permanent records has built one well-signposted vault – and a vault of exactly that shape was broken into by hackers in May 2025. Yours sits in your own Microsoft 365, behind your own locks – the record of truth is never vendor-owned.

If another vendor promises any of the above, ask them to put it in the contract. Ours is in writing, on the pricing page.
Explore the access feed and its tamper-evident record

Access transparency

An access feed you can inspect. Without the conversation content.

The access feed records administrative and operator events as a tamper-evident chain carrying counts, ids and settings, never message content. Each event carries the fingerprint of the one before it, so the chain can be re-checked from end to end by somebody who does not trust us, which is the correct posture for somebody buying this.

An operator Replay view can still open if writing its access event fails; that failure is logged on our side. Direct database break-glass access is refused if its event cannot be recorded. The full access controls and limitations are in DPA Annex D.

The whole chain is re-verified nightly, and again every time an administrator opens the feed. If it ever broke, the report would name the event it broke at rather than showing a green tick and hoping.

And you can take it away from us. One button downloads the entire content-free ledger as JSONL, one event per line, to hand to an auditor or to diff against the copy filed in your own tenant.

Client portalOakfield Trust
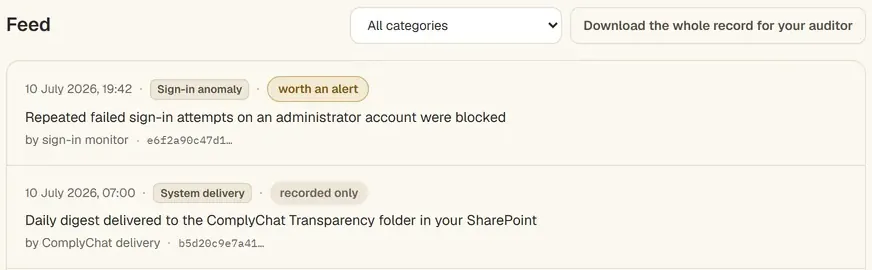
The access feed in the Trust and transparency pane of the ComplyChat client portal, headed by a filter and a button that downloads the whole record for an auditor, above two content-free events: a run of failed sign-ins on an administrator account that was blocked, and a daily digest delivered to the organisation's own SharePoint, each carrying its category, its source and the start of its chain fingerprint.
Your own feed · your own auditor's copy

Content-free hash-chained access-transparency ledger

Chain verification and broken-chain reporting · Access-transparency feed with chain re-verification · JSONL export of the whole transparency ledger

Chain verified end to end Chain broken at event 4 of 6

Access history6 linked events · Oakfield Trust
  1. 062026-08-21 09:14ZAdministrator opened a channel recordOakfield Trustc41f…9e2
  2. 052026-08-20 16:02ZRetention window changed to 90 daysOakfield Trust8b70…15d
  3. 042026-08-20 11:47ZDistribution log exported Oakfield Trust2ad9…f04
  4. 032026-08-19 08:30ZAn administrator was invitedOakfield Trustffe1…73c
  5. 022026-08-18 22:00ZDaily digest filed into your tenantOakfield Trust91c2…0aa
  6. 012026-08-18 07:55ZChannel created: Safeguarding - Year 7Oakfield Trust40de…b18

Nothing here is a message. Each row is an action, a count and a fingerprint.

The button on event 04 alters that row; the banner above then names the event the chain broke at.

The demo · from your own phone

Know where you stand before someone asks.

Ten minutes with our team. Bring your hardest case – the group nobody admits to, the leaver with two years of messages. In the first minute or two you'll be messaging in a real channel from your own phone; before we finish, a magic link signs you into your own client portal, where you can see your own record. Then a straight answer on whether we are right for you. Even if that answer is no.

The briefing: one page on the risks in your work messaging, written for boards. No follow-up unless you ask for one.